

Table of contents
In August 2026, a critical vulnerability was discovered in the popular Sourcerer extension from Regular Labs. The vulnerability allows an unauthenticated attacker to execute arbitrary PHP code on the server through unverified {source} blocks in the final HTML code of the page, leading to full site compromise.
The vulnerability has been assigned CVE-2026-74253 with a maximum CVSS v4.0 score of 10.0 (Critical). Attackers are already actively scanning the internet for vulnerable sites.
Regular Labs developers have released a complete fix in version 16.0.0.
Understanding the threat: what was fixed?
The vulnerability is an uncontrolled code generation flaw (CWE-94) in the Sourcerer extension. Unlike many other security flaws, this attack does not require authentication.
How the hack works:
- Processing {source} blocks: Sourcerer scans the final HTML code of the page for
{source}tags and executes the code contained within them (including PHP). - Lack of origin verification: The extension does not verify where this code originated — whether from trusted content (a Super Administrator's article) or from reflected user input.
- Insufficient origin verification: In vulnerable versions, the extension could not always reliably determine whether a block was saved by a trusted administrator or entered the page via an external request.
- Code execution: When the page loads, Sourcerer intercepts this block and executes PHP commands on the server.
- Outcome: The attacker gains full control over the site: database access, configuration modification, creation of hidden accounts, and use of the server for malicious purposes.
Who Is at risk?
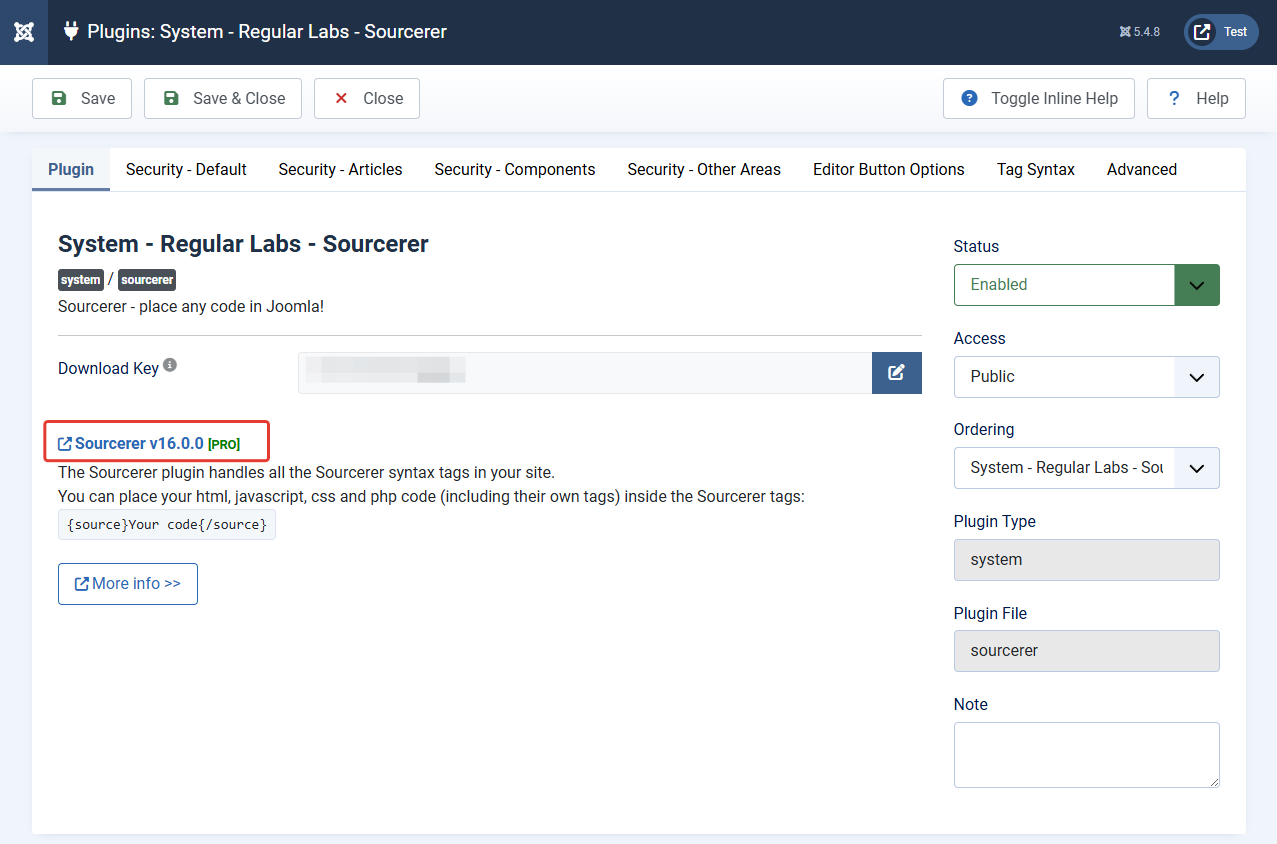
All sites running the Sourcerer extension versions below 16.0.0 are at risk, including all versions from 1.0.0 through 15.x.x.
How to fix It: step-by-step instructions
To address this vulnerability, follow the steps below.
Step 1: immediately update Sourcerer to version 16.0.0
- Go to your Joomla administrator panel and navigate to System → Update → Extensions.
- Click "Check" to search for updates.
- Locate the update for Sourcerer in the list.
- Update to version 16.0.0 or higher.
Step 2: сheck for Signs of Compromise
Installing the patch does not remove signs of compromise left before the update. A thorough inspection is necessary:
- Check all articles and content: Look for
{source}blocks in unexpected places, especially in areas that accept user input (forms, comments, search). - Check user accounts: In the Users section, sort the list by registration date. Find and delete any suspicious administrator accounts.
- Check site files: Pay attention to recently modified files in the root folder, especially
index.php,configuration.php, and files in the/mediaand/imagesfolders. - Check installed extensions: In the Extensions → Manage section, find and delete any suspicious plugins or components.
Step 3: additional Security Measures
In addition to updating the extension, we strongly recommend:
- Change all passwords: database password, FTP/SSH, hosting control panel, as well as passwords for all users with administrator privileges.
- Update the Joomla core to the latest version.
- Install and configure Admin Tools Pro: Generate a strict
.htaccessfile and activate injection protection. - Enable two-factor authentication for all accounts with administrator and editor privileges.
- Regularly create backups of your site.
We can do everything for you
If everything listed above seems too complicated, if you simply do not want to spend your time on it or if you would like to save money on expensive extensions, we are ready to help:
- update your website to the latest Joomla version together with all extensions used on it;
- audit the installed extensions and then remove those that are not being used;
- configure website backups, including backups to remote storage;
- install licensed versions of popular extensions on your website;
- protect your website from hacking by implementing additional security measures;
- take your website under our wing by regularly updating the CMS and all extensions, including commercial ones.